 Agent Isolation
From Shared Process Tree to Dedicated Guest Kernel What the Container-to-Micro-VM Transition Means for Agent State
Micro-VMs let agents keep their state without keeping compute.
Tobias Wrenfeld·
 Agent Isolation
Serverless Wrappers Versus Real Guest Kernels What Agent Isolation Claims Actually Deliver at Runtime
Guest kernels stop kernel exploits from crossing to neighbors.
Céleste Mouamba·
 Agent Isolation
Failure Modes That Emerge When Hundreds of Concurrent Agents Share a Kernel Instead of Owning One
Shared kernels expose agents to cross-boundary failures no isolation plan prevents.
Jin-ho Baek·
 Agent Isolation
Why Shared Infrastructure Agent Deployments Fail Without Guest Kernel Ownership
Guest kernels isolate agent code execution where shared containers cannot.
Tobias Wrenfeld·
 Agent Isolation
Why Multi-Tenant Agent Clouds Need Hardware Virtualization Boundaries Not Namespace Tricks
Hardware virtualization boundaries, not namespaces, can contain agents executing untrusted code.
Priya Subramaniam·
 Agent Isolation
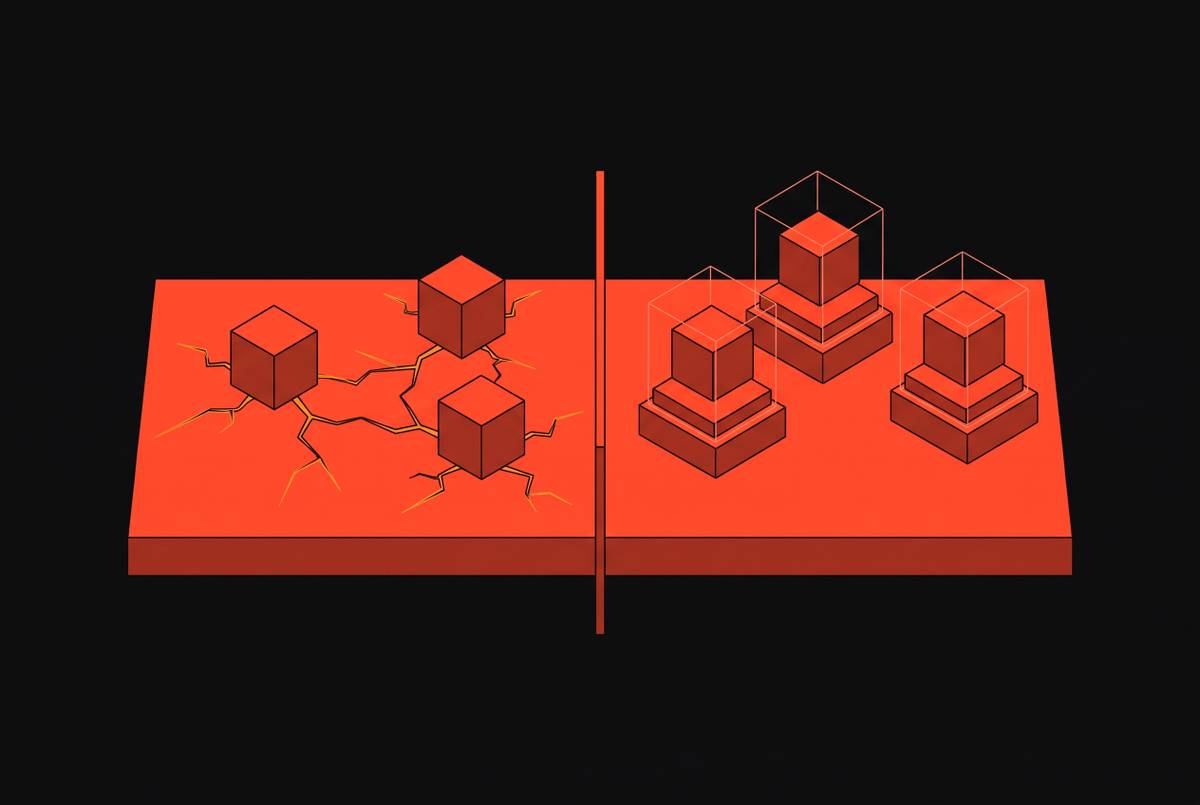
Why the Host Kernel Is Your Biggest Agent Security Liability and How Micro-VMs Fix It
Separate guest kernels stop LLM-generated code from reaching your host infrastructure.
Céleste Mouamba·
 Agent Isolation
Runtime Isolation Options for Untrusted AI Agents Ranked by Blast Radius
Ranking isolation methods by how much damage a compromised AI agent can actually cause.
Jin-ho Baek·
 Agent Isolation
Outbound DNS and IP Filtering for Sandboxed Agent Networks
DNS and IP filtering must work together to prevent sandboxed agents from exfiltrating data.
Tobias Wrenfeld·
 Agent Isolation
Audit Logging for Actions Taken by Isolated AI Agents
Host-side isolation logs what agents do without trusting their own records.
Priya Subramaniam·
 Agent Isolation
Secret Injection Patterns for Isolated Agent VMs
Isolating agents requires per-VM credentials kept outside the process environment.
Jin-ho Baek·
 Agent Isolation
Inter-Agent Communication Security in Multi-Agent Systems
Poisoned messages between agents can trigger cascading failures across isolated systems.
Priya Subramaniam·
 Agent Isolation
Network Egress Controls for Isolated Agent VMs
Prompt-injected agents need egress controls more than compute sandboxing.
Céleste Mouamba·
 Agent Isolation
Prompt Injection Risks in Agents With Real Filesystem Access
Agents with file access turn prompt injection into remote code execution.
Tobias Wrenfeld·
 Agent Isolation
Safe Package Installation Inside Agent Sandboxes
Multiple layers of isolation and policy controls replace the human judgment that AI agents bypass.
Céleste Mouamba·
 Agent Isolation
Browser Session Isolation for Autonomous Web Agents
Prompt injection poses risks that traditional browser sandboxing wasn't designed to address.
Priya Subramaniam·
 Agent Isolation
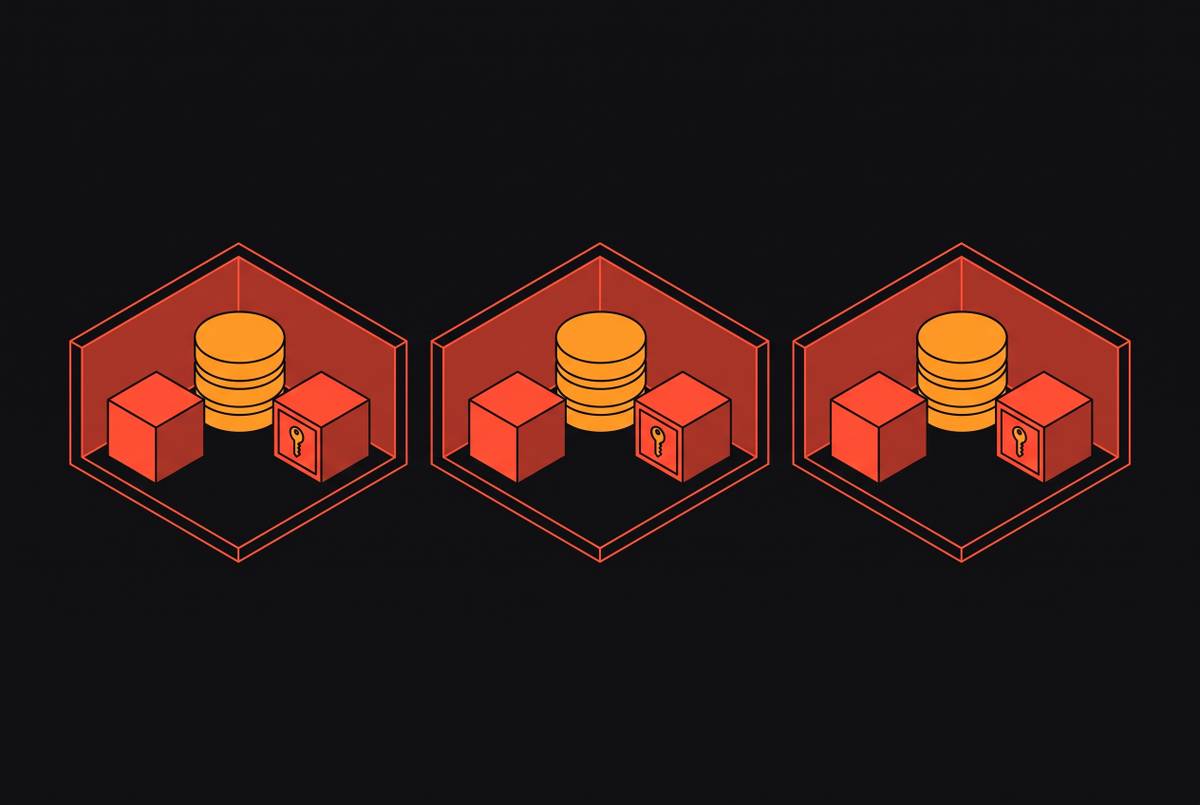
Per-Agent Filesystem Isolation and Credential Segregation
Closing security gaps requires both filesystem isolation and credential segregation together.
Tobias Wrenfeld·
 Agent Isolation
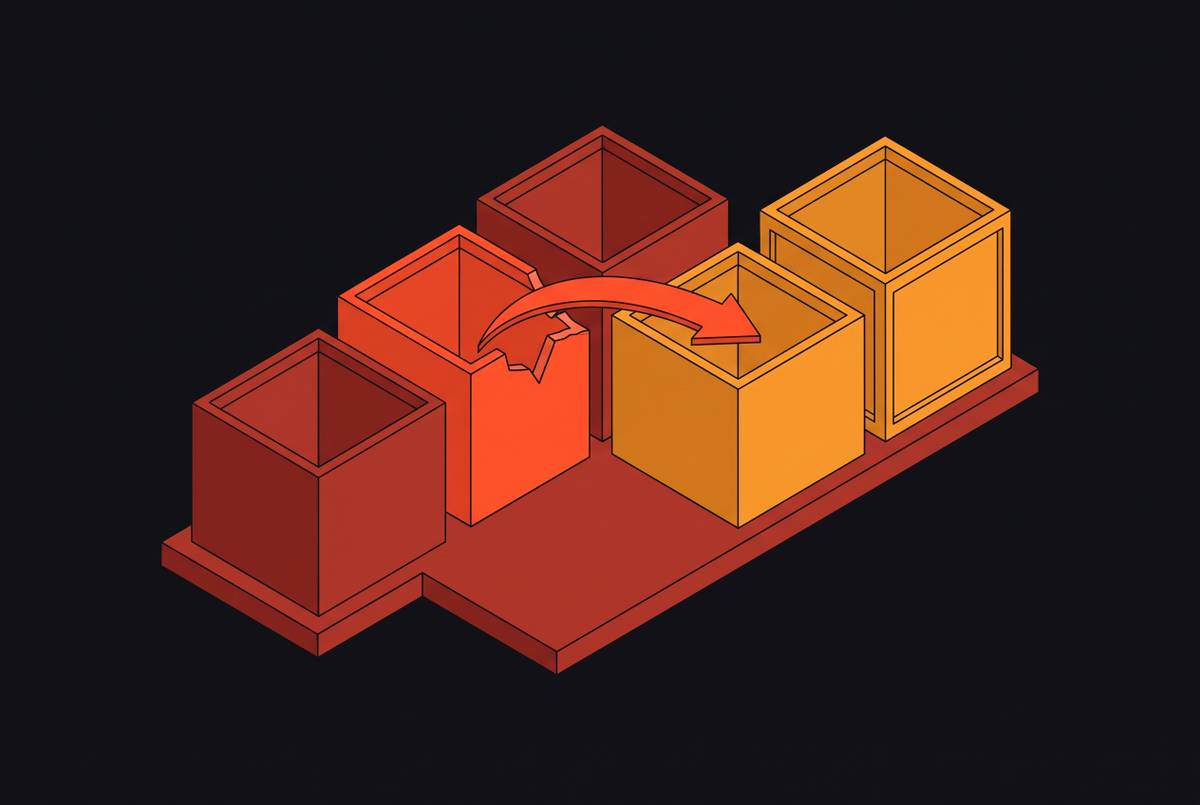
Escape Vectors in Shared Container Agent Runtimes
Containers share a kernel, and agents can exploit that to escape.
Jin-ho Baek·
 Agent Isolation
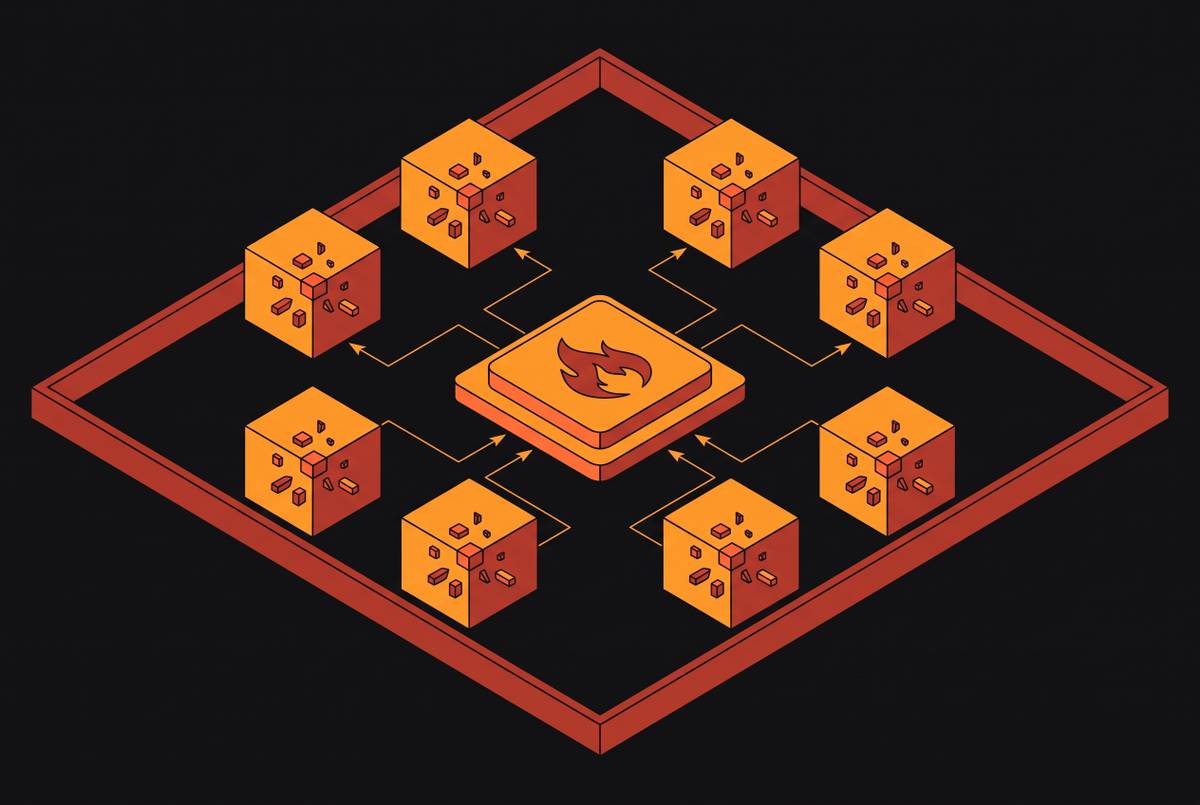
Kernel-Level Sandboxing for AI-Written Code Execution
Shared kernels are the wrong trust boundary for attacker-shaped code.
Céleste Mouamba·
 Agent Isolation
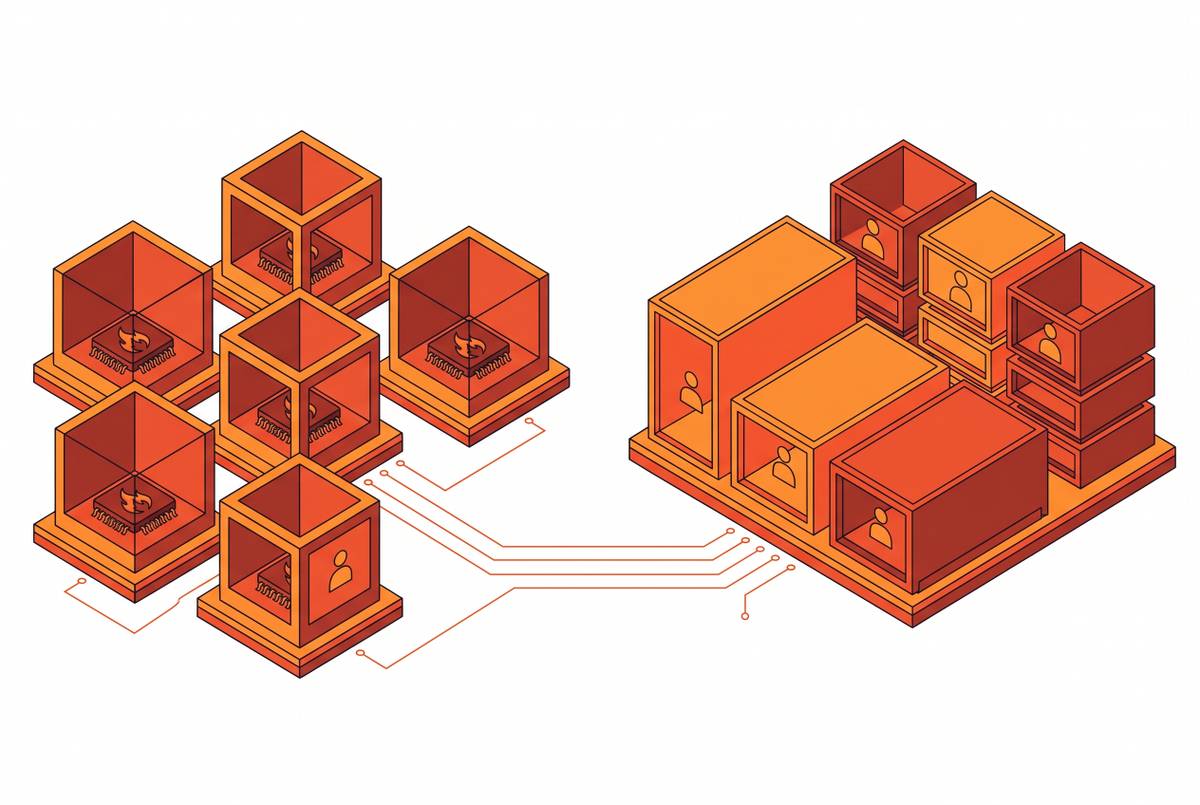
Firecracker Micro-VM Isolation vs Container Sandboxing for AI Agents
Micro-VMs stop kernel exploits that containers can't, at a cost.
Tobias Wrenfeld·